https://sudonull.com/top-cve-march-2026-rce-in-cisco-and-langflow
Critical vulnerabilities March 2026: Cisco FMC deserialization, Langflow RCE, Chrome zero-day, Trivy supply chain. Patches, exploits, mitigation for DevSecOps. Update systems now.
https://sudonull.com/top-cve-march-2026-rce-in-cisco-and-langflow
Critical vulnerabilities March 2026: Cisco FMC deserialization, Langflow RCE, Chrome zero-day, Trivy supply chain. Patches, exploits, mitigation for DevSecOps. Update systems now.
https://sudonull.com/cve-2024-51378-cyberpanel-rce-vulnerability
Analysis of command injection in CyberPanel up to 2.3.7. Step-by-step exploitation, PoC code, protection measures. Update the panel to eliminate RCE risk.
https://sudonull.com/cve-2024-48990-lpe-in-needrestart-linux
Analysis of CVE-2024-48990 vulnerability in Needrestart: LPE mechanism via PYTHONPATH, PoC exploit, patching. Instructions for middle/senior devops. Check the system.
https://sudonull.com/cve-2026-4247-freebsd-tcp-dos-vulnerability
Analysis of CVE-2026-4247: mbuf leak in TCP Challenge ACK FreeBSD. Attack vectors, sysctl fix, branch patches. Update systems to protect against remote DoS.
https://sudonull.com/marimo-cve-2026-39987-vulnerability-key-theft-in-3-minutes
Critical hole in Marimo allows hackers to steal cloud keys without authorization. Learn exploitation details, risks and how to protect systems. Update urgently — read the analysis.
NVD-CVE-2010-3971
https://nvd.nist.gov/vuln/detail/cve-2010-3971
This service is down at the moment. Please try again later.
CVE-2010-3971 - Vulnerability Details - OpenCVE
https://app.opencve.io/cve/CVE-2010-3971
Authentication None Confidentiality Impact Complete Integrity Impact Complete Availability Impact Complete This CVE is not in the KEV list. The EPSS score is 0.856. Key SSVC decision points have not yet been added.
Exploit:Win32/CVE-2010-3971 threat description - Microsoft ...
https://www.microsoft.com/en-us/wdsi/threats/malware-encyclopedia-description?Name=Exploit:Win32/CVE-2010-3971
Jan 4, 2011 · Exploit:Win32/ CVE - 2010 - 3971 is the detection for a vulnerability in Internet Explorer. The vulnerability exists due to the creation of uninitialized memory during a CSS function within Internet Explorer.
Microsoft Security Advisory 2488013 | Microsoft Learn
https://learn.microsoft.com/en-us/security-updates/securityadvisories/2010/2488013
Dec 22, 2010 · To improve security protections for customers, Microsoft provides vulnerability information to major security software providers in advance of each monthly security update release.
CVE-2010-3971 - GitHub Advisory Database
https://github.com/advisories/GHSA-r6fx-qpgx-pg2w
May 12, 2022 · Use-after-free vulnerability in the CSharedStyleSheet::Notify function in the Cascading Style Sheets (CSS) parser in mshtml.dll, as used in Microsoft Internet Explorer 6 through 8 and other products, allows remote attackers to execute arbitrary code or cause a denial of service (application crash) via a self-referential @import rule in a stylesh...
CVE Record: CVE-2010-3971
https://www.cve.org/CVERecord?id=CVE-2010-3971
Service is currently unavailable. Please report the issue and try again later. Or, use Search CVE List on cve .mitre.org to search CVE Records. Sorry for the inconvenience.
CVE-2010-3971 | Tenable®
https://www.tenable.com/cve/CVE-2010-3971
Jun 16, 2026 · Use-after-free vulnerability in the CSharedStyleSheet::Notify function in the Cascading Style Sheets (CSS) parser in mshtml.dll, as used in Microsoft Internet Explorer 6 through 8 and other products, allows remote attackers to execute arbitrary code or cause a denial of service (application crash) via a self-referential @import rule in a stylesh...
Learn how does retrieval augmented generation work: RAG reduces AI hallucinations, grounds responses in real data, and transforms LLMs into trustworthy systems. Start now.
Learn how to use React hooks effectively with practical examples. Master useState, useEffect, useContext, and custom hooks in this complete guide for modern React.
Learn what is Kubernetes and how it works. Understand its architecture, self-healing, scaling benefits, and real-world impact. Start mastering container orchestration today.
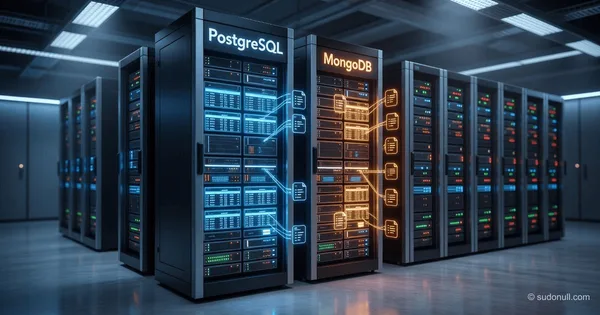
MongoDB vs PostgreSQL when to use each: compare ACID compliance, scalability, schema flexibility, and query power. Choose the right database for your project.
Learn how to implement JWT authentication securely in your web API. This complete guide covers token issuance, validation, best practices, and production security.
Analysis of EIC Tech Report 2026: 25 early deep-tech signals to strengthen Europe. Bio-inspired AI, quantum communications, biomineralization, and surgical robotics. Who wins and who loses? Read the full review.
Learn how to design RESTful APIs for web applications with best practices on URIs, HTTP methods, versioning, and documentation. Build scalable, intuitive APIs that developers love.
JavaScript vs Python which is better for you? Compare ease of learning, salaries, use cases, and career paths to choose the right first language in 2026. Start now.
Learn how to build an AI agent with LangChain in this step-by-step tutorial. Set up tools, integrate LLMs, and create autonomous agents with memory.
Chinese startup DeepWay announced a robotaxi with a range of 1000 km on solid-state batteries. Learn how this changes the electric vehicle market and why it matters.